
One signature, zero bridges. Maat settles cross-chain transfers from Arbitrum via ZK proof. No wrapped tokens, no destination gas. Live on testnet today.
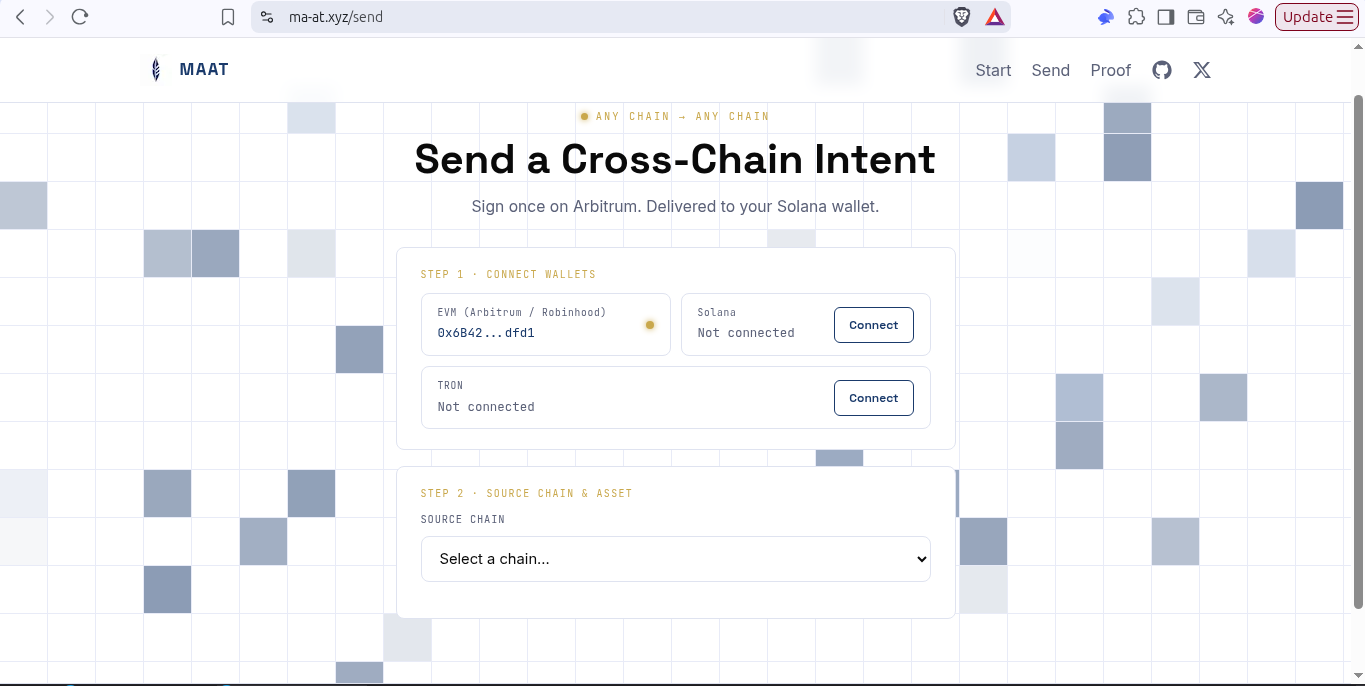
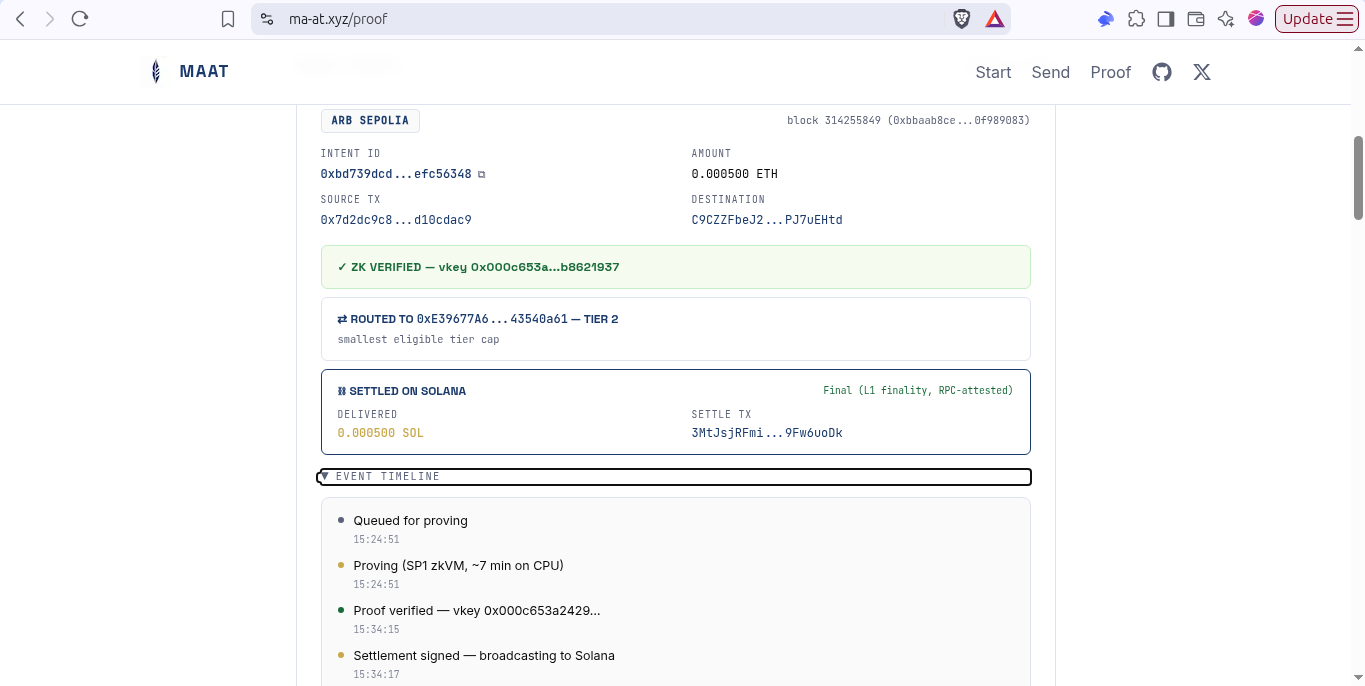
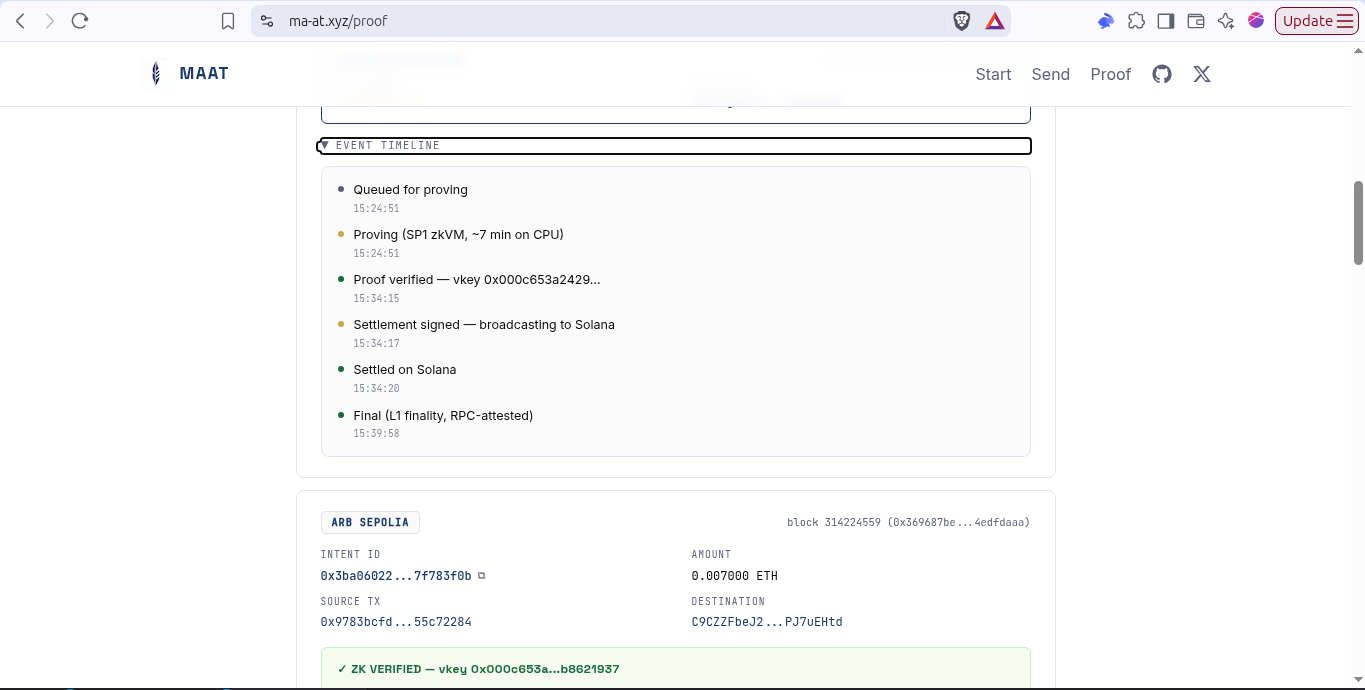
Maat is a ZK-verified cross-chain intent network. You sign once on Arbitrum: no bridging, no wrapped tokens, no gas on the destination chain. A solver fronts your funds on the destination chain and gets repaid once an SP1 zero-knowledge proof confirms your Arbitrum transaction finalized. Every solver is tiered and collateralized against live on-chain state before it's trusted with funds. I'm translating ten years of credit-risk underwriting experience and applying to solver counterparty risk, not just the UX layer. Live today: Arbitrum Sepolia → Solana Devnet, two independently tiered solvers routing real intents.
IntentManager.sol deployed and live on Arbitrum Sepolia. Two tiered solvers routing real intents end-to-end. A small transfer auto-routed to the lower-capacity solver, a larger one to the higher-tier solver, both ZK-proof verified and settled on Solana. Found and fixed three real issues this week: two fund-lock edge cases in the settlement contract, one wrongly-triggered solver slash (stale on-chain state check), and a process-handoff bug that could stall back-to-back proofs. Proof generation runs ~7 min per intent (currently running CPU audits, due to time contraints); full audit not yet done. However, our internal agent GlassOfBeer is the one that audited and performed a whitehat exploit on the contracts to find the bugs and security lapses. I'm stating both plainly, nothing hidden.
Note: You'll see a fork of the repo by GlassOfBeer the updated bug free and exploit audited contracts are in that fork.
Self-funded, bootstrapped build. Not currently running a raise. Planning to apply to Arbitrum Foundation and Solana Foundation ecosystem grants post-hackathon.