
ChainGuard
Tokens that screen their own transfers: one on-chain threat registry blocks hackers, drainers & sanctioned wallets across Arbitrum and Robinhood Chain, synced in ~4 s.
Videos
Tech Stack
Description
ChainGuard — on-chain compliance firewall for stablecoins and tokenized stocks.
THE PROBLEM
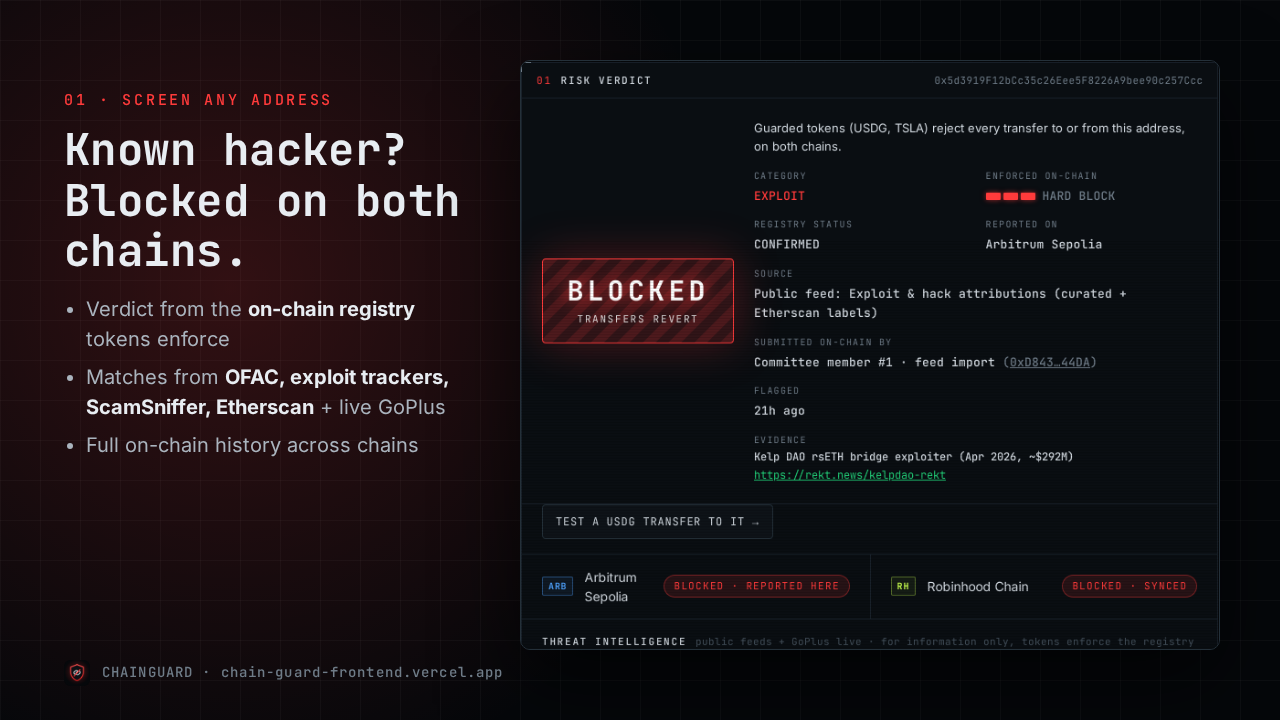
A broker must screen who it trades with. An ERC-20 screens no one. As stock tokens on Robinhood Chain and stablecoins like USDG bridge regulated finance and DeFi, an address behind a $292M bridge exploit, a phishing drainer or an OFAC listing can still receive and trade them. Today the only response is off-chain, after the fact.
THE SOLUTION
ChainGuard moves screening into the token itself:
• ComplianceRegistry — one on-chain list of risky addresses: category (sanctioned, exploit, phishing, mixer, rug pull, scam), severity 1–3, evidence, reporter, governance status.
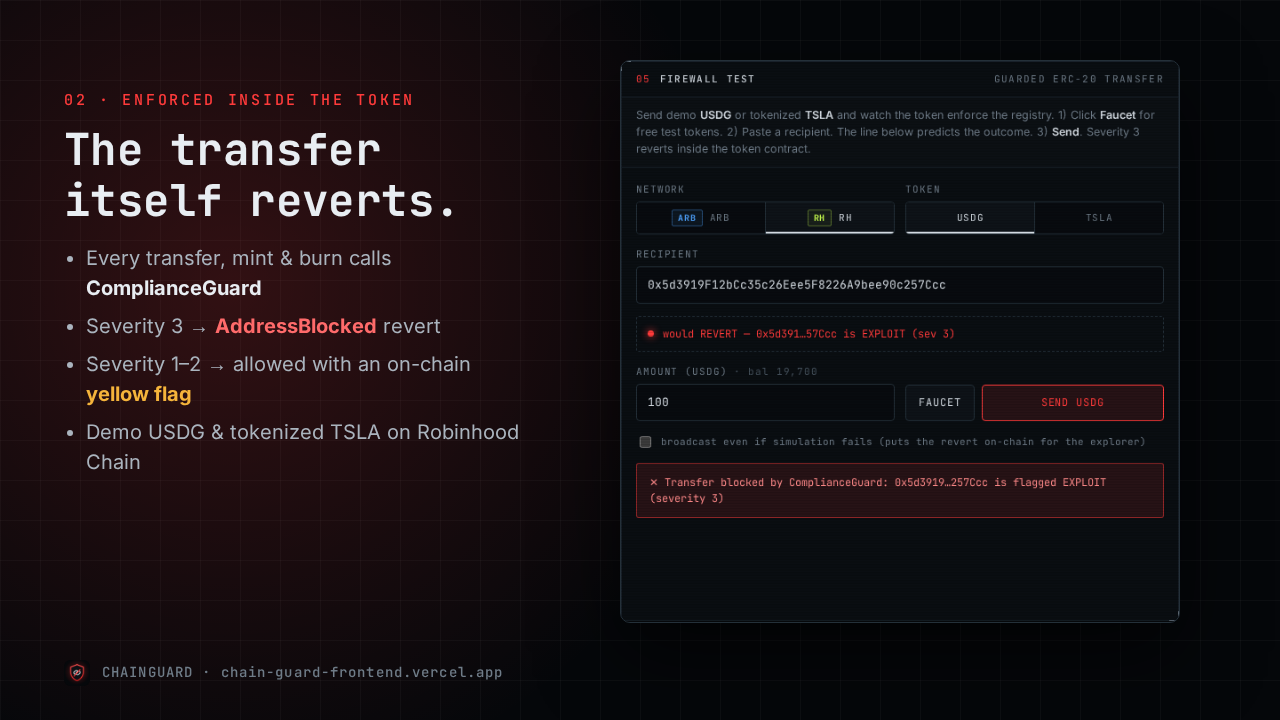
• ComplianceGuard — a transfer hook any token plugs into. Severity 3 → the transfer reverts with AddressBlocked(account, category, severity). Severity 1–2 → it goes through with an on-chain ComplianceWarning ("yellow flag").
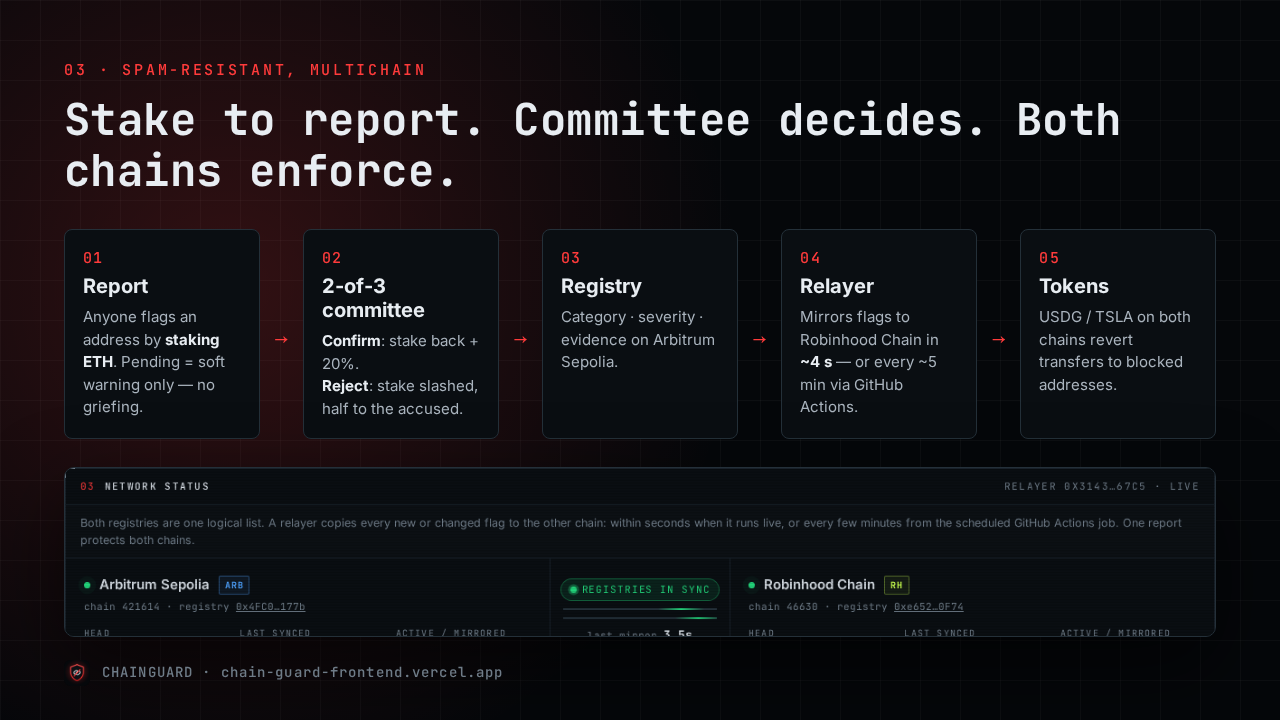
• Staked reporting — anyone can report by staking ETH. A 2-of-3 committee confirms (stake back + 20% reward) or rejects (stake slashed: half to the wrongly accused address, half to the reward pool). Until confirmed a report is only a soft warning, so nobody can freeze funds by griefing. Appeals and expiry included.
• Multichain — one logical registry on Arbitrum Sepolia and Robinhood Chain testnet. A relayer mirrors every flag with replay/ordering/conflict protection: 3.95 s measured from quorum on Arbitrum to block on Robinhood. A scheduled GitHub Actions job keeps chains in sync with no server running.
• Real threat data — 10,232 labelled addresses from OFAC, exploit attributions (Kelp DAO, Bybit, Ronin, Multichain, Nomad…), ScamSniffer, Etherscan, MyEtherWallet and on-chain-verified Tornado Cash pools; 1,033 high-value entries enforced on-chain. Every lookup also queries GoPlus live (SlowMist, BlockSec).
TRY IT
Live: https://chain-guard-frontend.vercel.app — click "Kelp DAO exploiter" (BLOCKED on both chains), then send demo USDG to it in Firewall test: the token reverts.
Progress During Hackathon
Built from scratch during the hackathon:
• Smart contracts: ComplianceRegistry (staking, 2-of-3 committee, appeals, expiry, pull payouts, batch import, cross-chain mirroring), ComplianceGuard, guarded ERC-20 base, demo USDG and tokenized TSLA. 26 Foundry tests incl. fuzzing of stake accounting.
• Deployed and verified on Arbitrum Sepolia and Robinhood Chain testnet (Blockscout).
• Relayer (Bun + viem): batched mirroring, restart-safe, live mode (~4 s sync) and one-shot mode running every ~5 min on GitHub Actions — verified end-to-end with the local relayer switched off.
• Threat-intel pipeline: compiled 10,232 real addresses from 7 public sources; imported 1,033 high-value threats on-chain via committee batch votes and mirrored them to both chains.
• Web app (React + wagmi/viem, no backend): address verdicts with plain-language explanations, threat-feed matches, on-chain history, live event feed, cross-chain sync status, firewall test, staked reporting, committee desk, searchable registry, onboarding walkthrough. Deployed on Vercel.
• Verified on testnet: transfers to the Kelp DAO exploiter revert on Robinhood Chain; transfers to clean addresses pass.
Fundraising Status
Not raised. Bootstrapped hackathon project. Open to grants and ecosystem support (Arbitrum, Robinhood Chain) to move from a trusted relayer to native cross-chain messaging, add committee governance, and pilot integration with a stablecoin or tokenized-asset issuer.