
Privacy-Preserving AI Code Auditor — Run security audits inside 0G TEE enclaves, store results on decentralized storage, and get tamper-proof on-chain certificates.
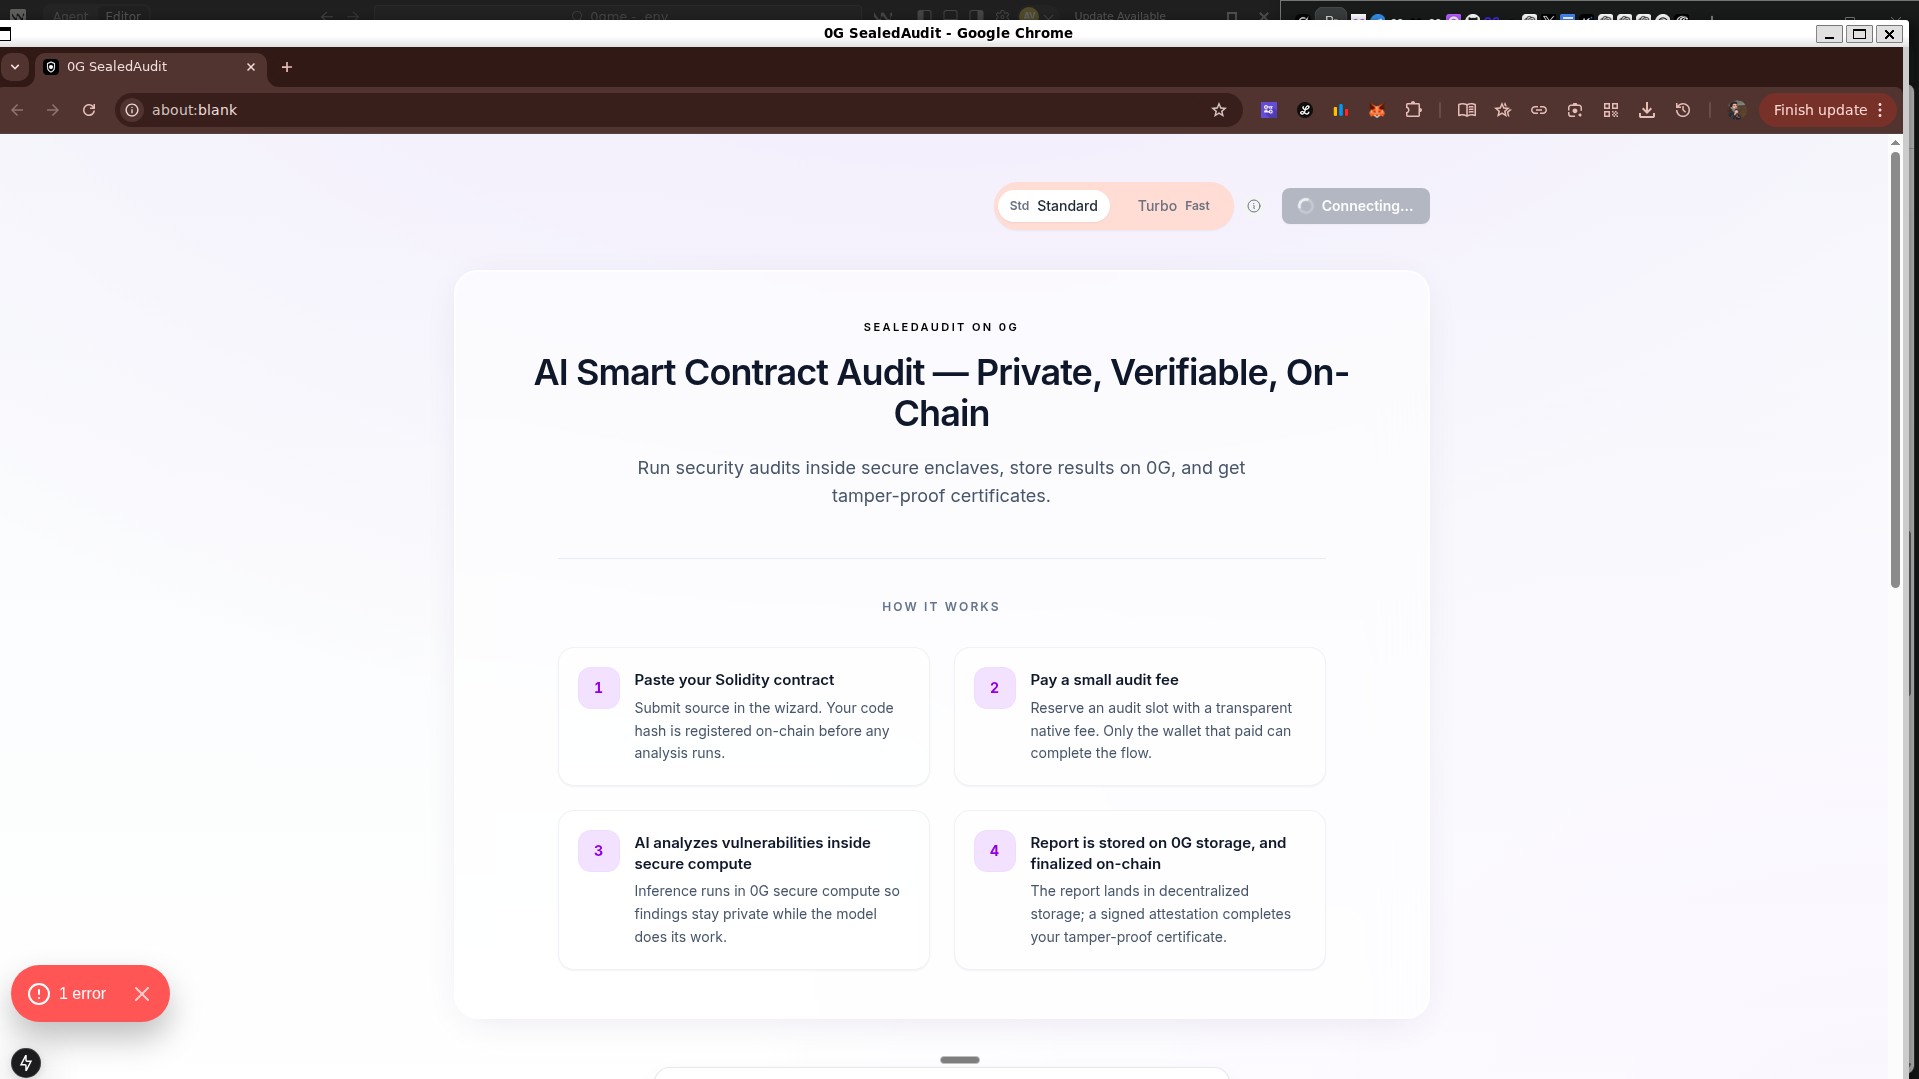
0G SealedAudit is a decentralized AI-powered smart contract auditor that solves the critical dilemma Web3 developers face: human audits cost $10,000+ and take weeks, while centralized AI services risk exposing proprietary code to IP leaks and front-running.
How it works:
Developers submit Solidity code via web UI or CLI (0g-audit)
Pay a small micropayment (0.001 0G tokens) to the smart contract
Code is analyzed inside 0G's Trusted Execution Environment (TEE) — ensuring hardware-level privacy
AI detects vulnerabilities (Reentrancy, Access Control, etc.) using specialized 0GSKILLS context
Audit report is permanently stored on 0G Storage with cryptographic Merkle proofs
Tamper-proof certificate is anchored on-chain with ECDSA attestation signatures
Key 0G Integrations:
0G Compute (Sealed Inference): TEE-backed AI execution for private vulnerability detection
0G Storage: Permanent archiving of audit reports with cryptographic proofs
0G Galileo Testnet: Smart contract registry for micropayments and certificates
Day Progress
Day 1 Deployed SealedAudit.sol smart contract on 0G Galileo Testnet (0xd52a4FDc194D28f93922043f87e1C01B4d4E9813). Implemented micropayment escrow system with prepaid/withdraw functionality. Built Next.js frontend with wallet connection.
next day 2 Integrated 0G SDKs (@0glabs/0g-serving-broker, @0glabs/0g-ts-sdk). Built OpenClaw agent orchestration flow. Implemented TEE attestation signing with ECDSA verification. Created CLI tool (0g-audit) for power users.
after 3 days Added 0G Storage integration for permanent report archiving. Built certificate dashboard with on-chain verification. Implemented complete end-to-end audit flow from code submission → TEE analysis → storage anchoring → certificate generation.
Current: Pre-seed / Hackathon project
Status: Bootstrapped, seeking grants and early investment post-hackathon