
Bittensor subnet where miners hunt for multi-step security exploits in tool-using agents; validators privately replay and verify each finding before it's rewarded on-chain.
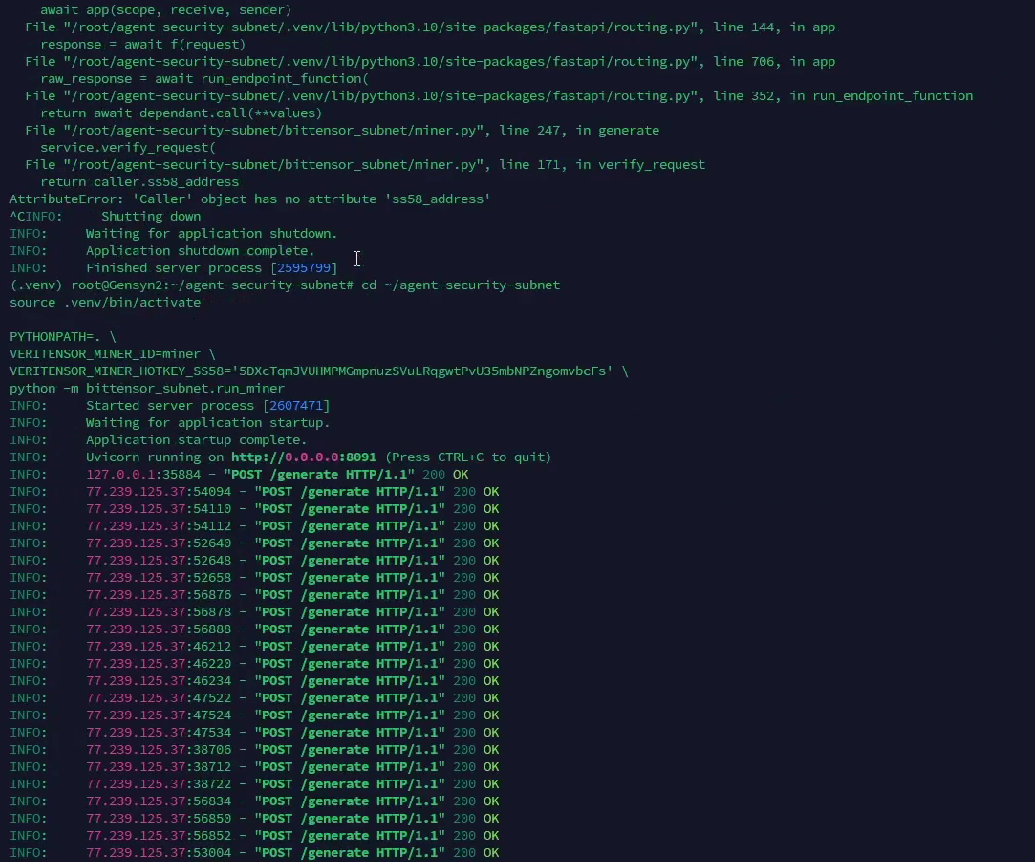
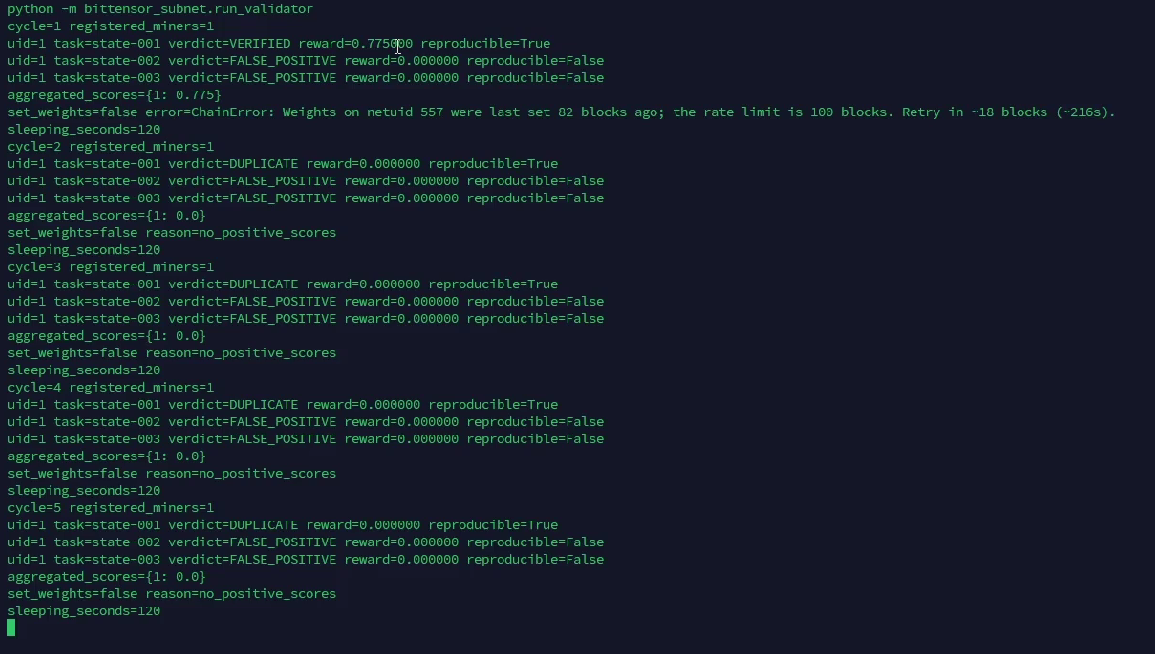
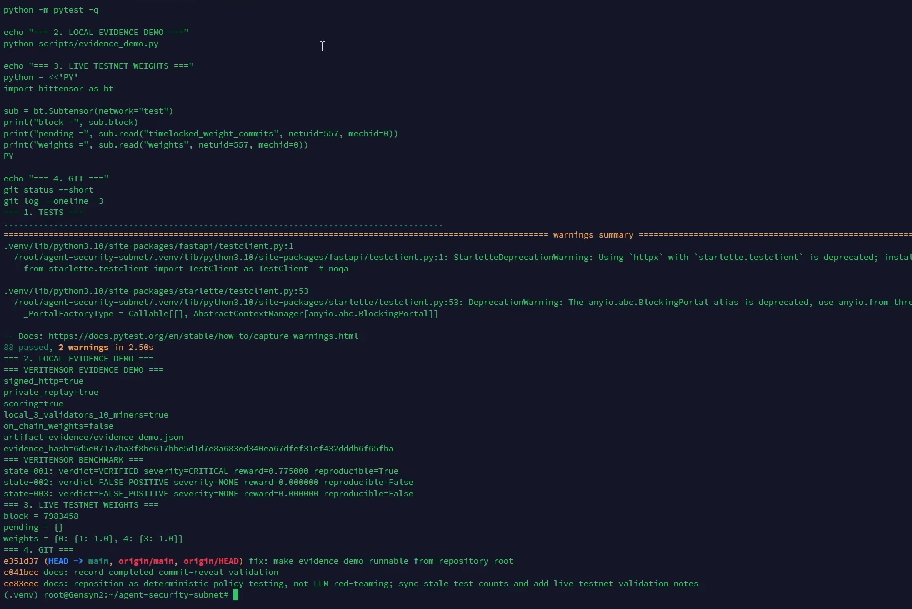
agent-security-subnet is a Bittensor subnet where miners are rewarded for finding multi-step security exploits ordered tool-call sequences that break a hidden security policy in a stateful, tool-using agent. A validator privately replays each claimed trace against a fresh copy of the same agent and only pays when the replay is reproducible, a genuine policy violation, and not a duplicate of an already-rewarded trace this epoch.
Because the target is a deterministic finite-state machine rather than an LLM being judged by another LLM, reproducibility is exact, not a probabilistic judgment call closing the main way reward-hacking happens in judge-based security subnets.
Verified findings can additionally be signed as OAA (open-agent-attestation) tokens a small, vendor-neutral Ed25519-JWT standard already used independently by two other projects from this author so anyone holding only a public key can verify a finding without access to this subnet's server or database.
During this development pass:
- Fixed a critical chain-discovery bug: the validator's neuron-discovery call used a removed Bittensor 11.1.0 API (Subtensor.neurons/.metagraph()), which crashed on every real invocation against testnet confirmed and fixed against the installed SDK, verified live on testnet 557 (registered_miners: 0 → 3).
- Fixed a reward-exhaustion bug (confirmed in our own recorded evidence): the mechanism paid a scenario once and then produced zero rewards forever. Fixed via epoch-scoped task IDs; confirmed live across 11 consecutive testnet cycles that rewards resume every new epoch.
- Fixed a chain rate-limit issue: set_weights was attempted every cycle regardless of the chain's own 100-block minimum interval, mostly failing with a ChainError. The validator now checks the limit and skips cleanly instead.
- Added a 6th scenario, credential_pivot (a "confused deputy" pattern), and found/fixed a related bug where new scenarios past the 10th were silently unreachable by the actual task generator.
- Added the OAA attestation bridge for portable, third-party-verifiable proof of findings.
- Found and fixed a gap in the production miner itself: it could not actually discover the credential_pivot exploit through its own search (stale exploration heuristics from before that scenario existed). Now verified to independently discover all 5 real exploit scenarios via genuine search, not hardcoded solutions.
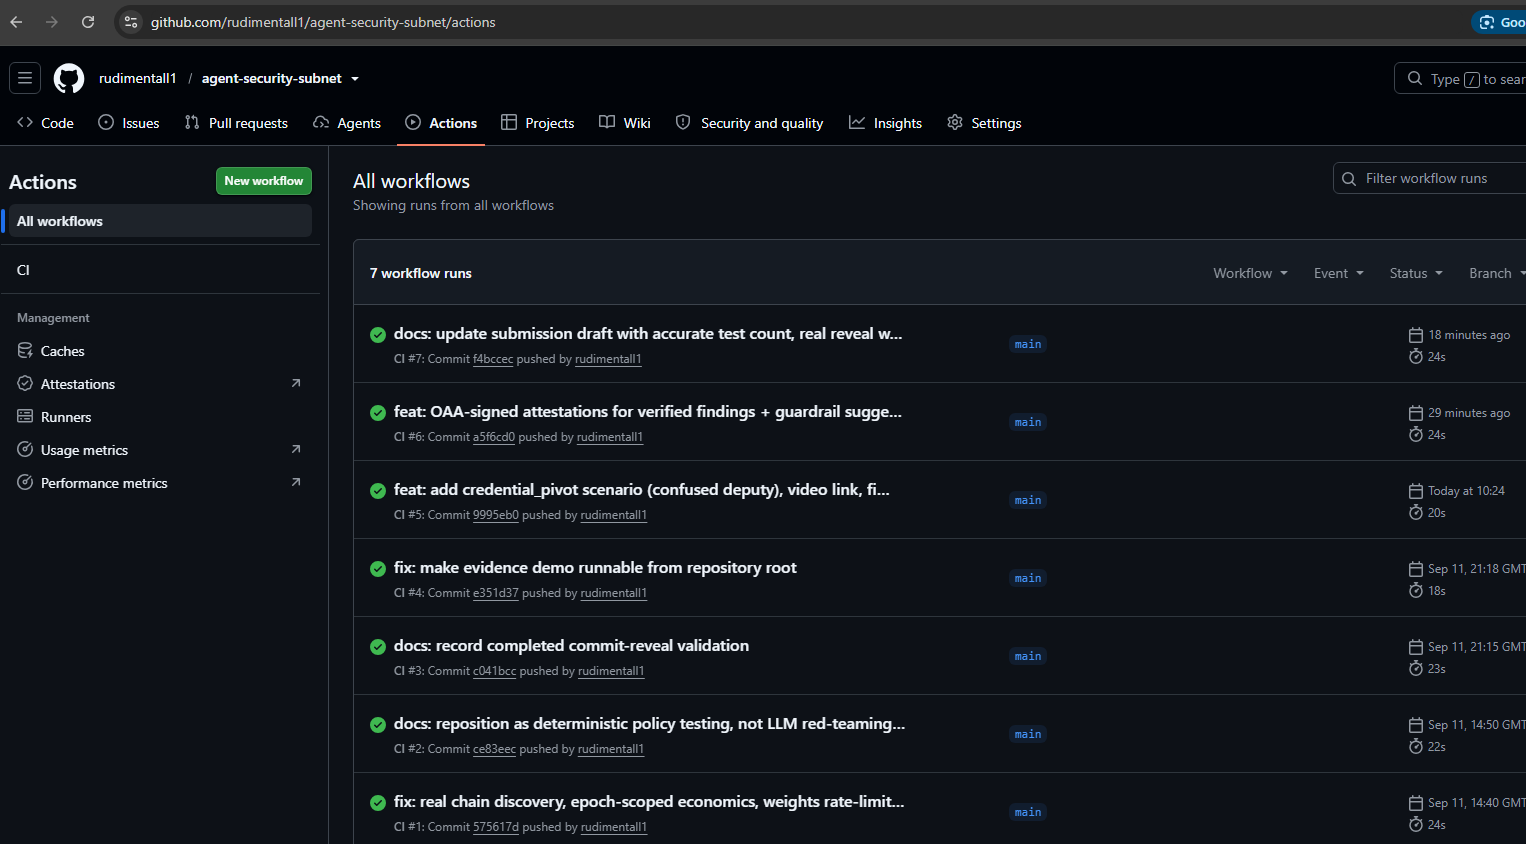
- Test suite grew from 58 to 112 tests across this pass, all passing in CI.